Identity-driven access intelligence

See who has access to what and why

Understand what every human and non-human identity can actually access across your enterprise, what they can do, and the permissions and relationships that make that access possible.

Request a Demo
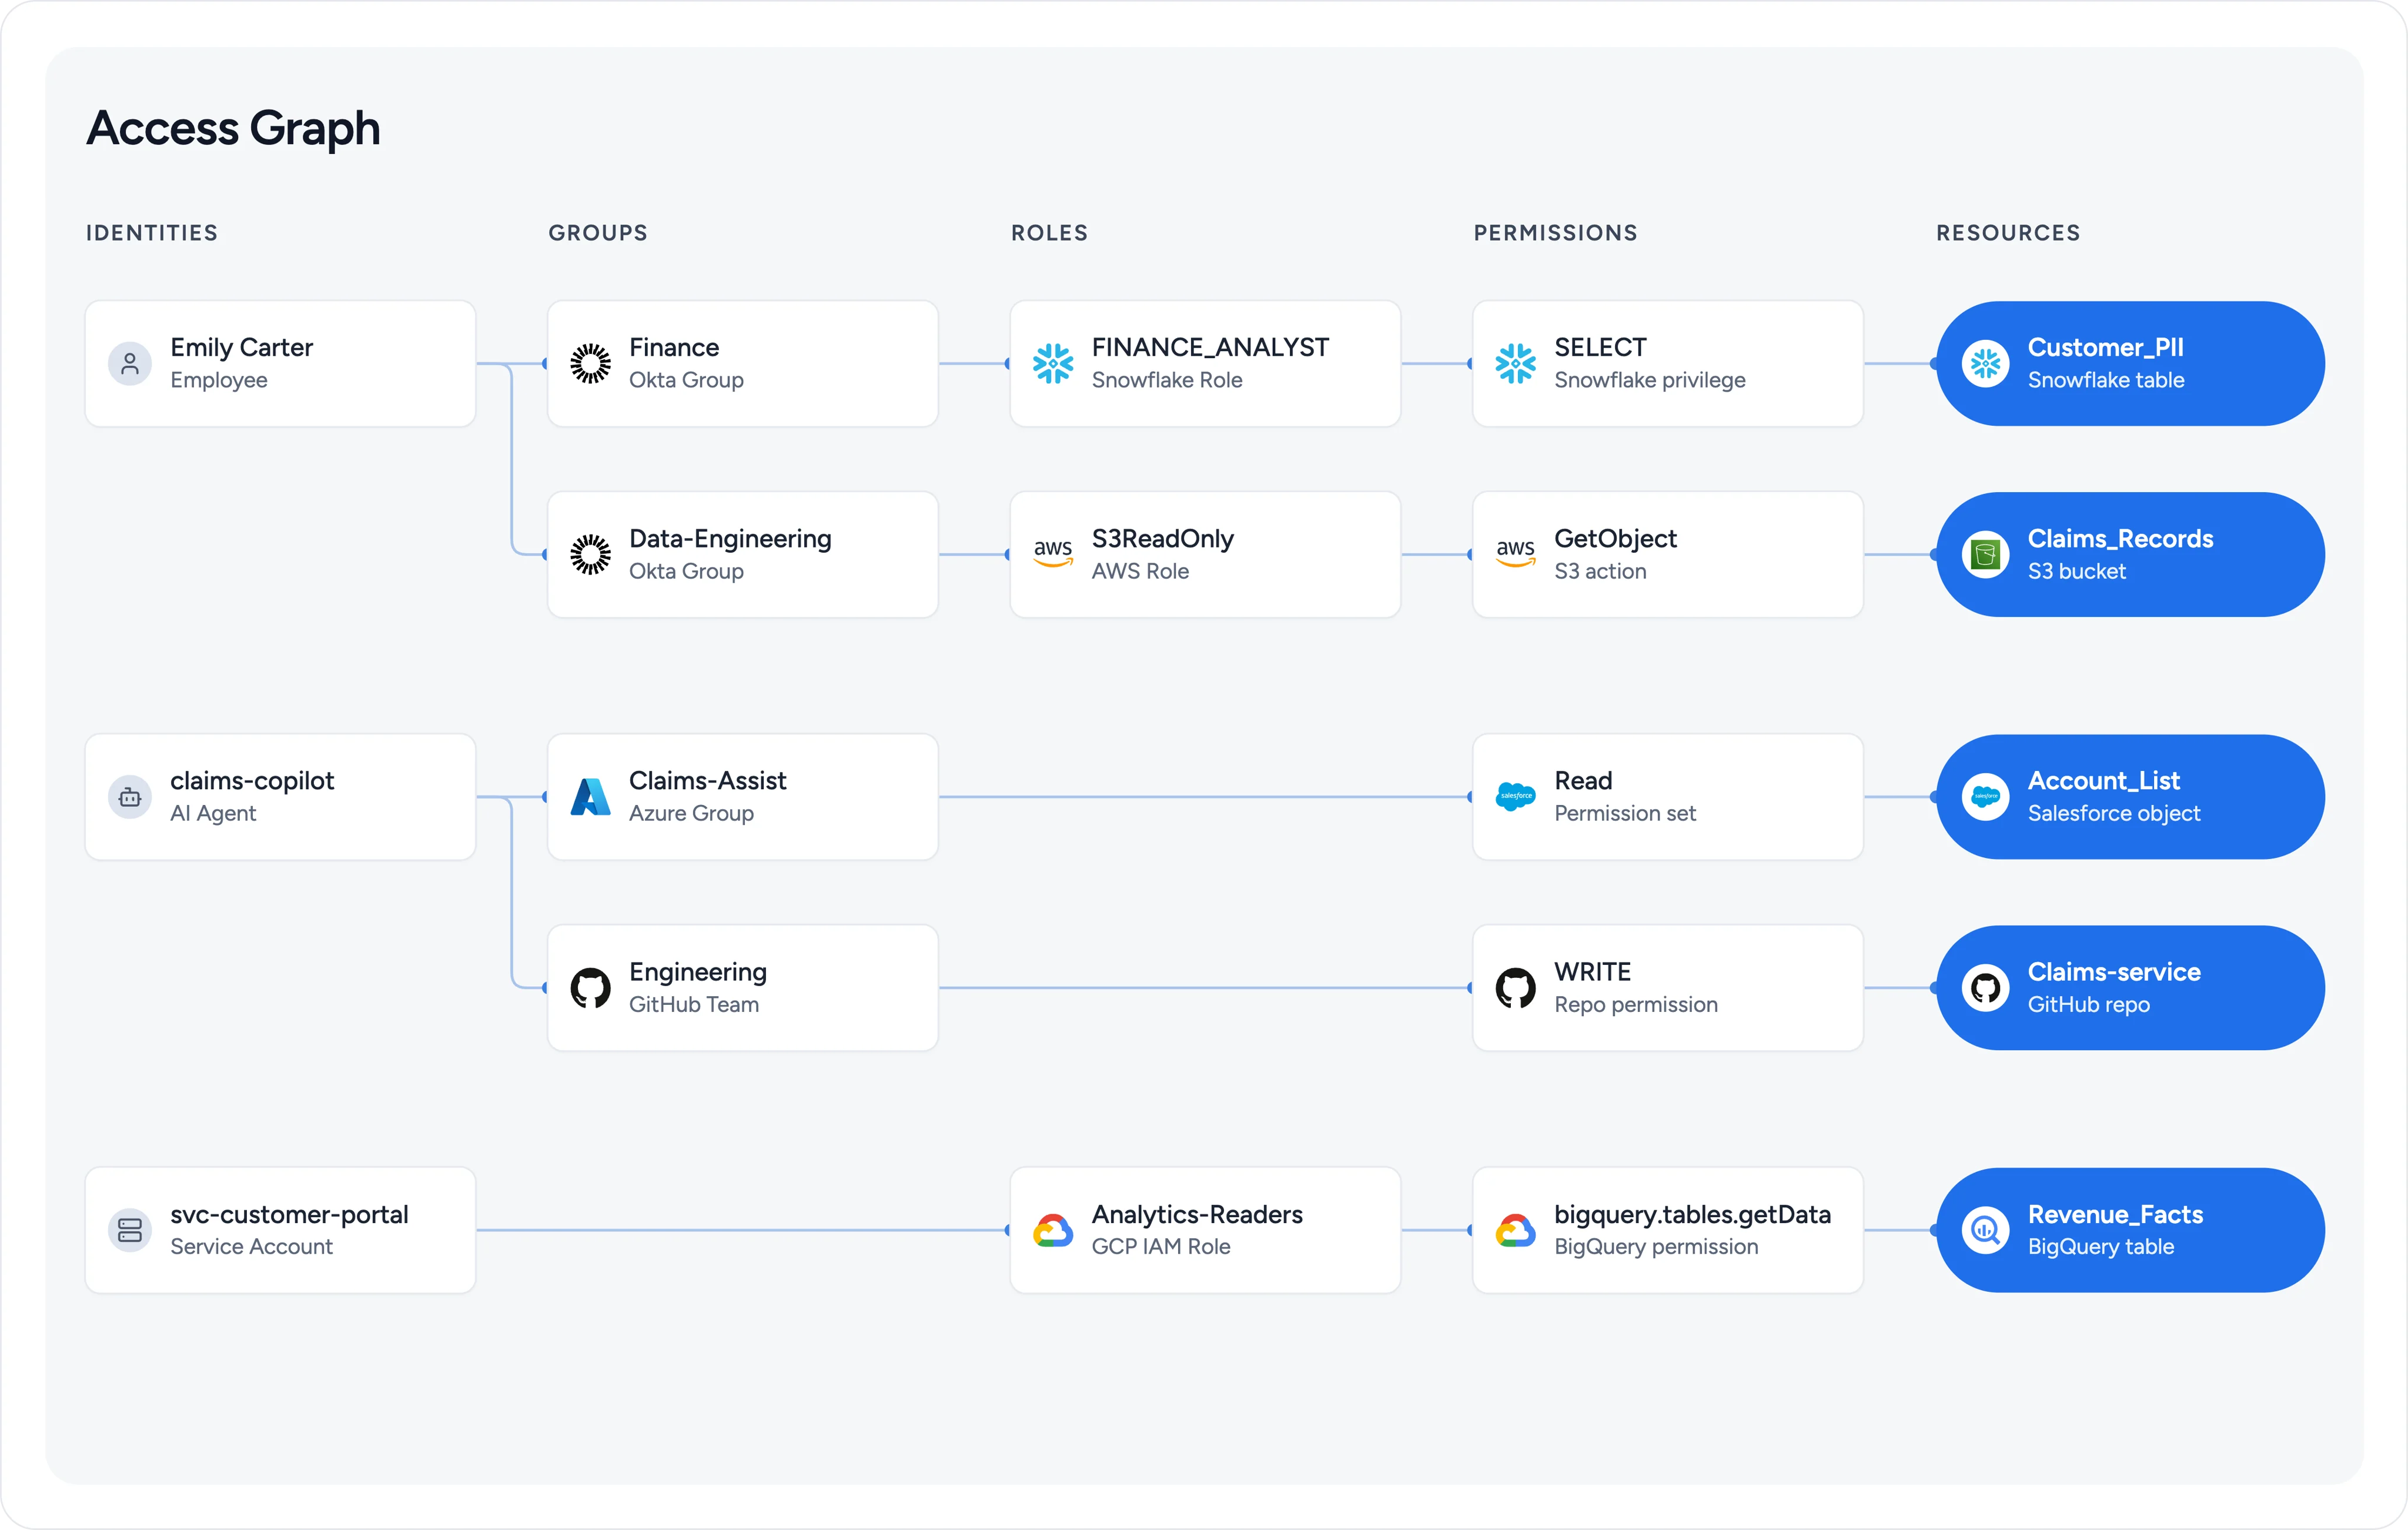
Ubiq Access Intelligence graph showing human identities, service accounts, applications, workloads, and AI agents connected through groups, roles, permissions, and resources

Effective permissions analysis for ISPM

Identity security posture management (ISPM) needs a view of what identities can actually access. Ubiq resolves direct assignments, groups, nested roles, policies, inherited permissions, and other authorization paths across supported systems. Investigate effective permissions for human and non-human identities and identify excessive access with the available evidence.

Effective permissions

  • Understand effective access: See what every human and non-human identity can actually access and what actions they can perform.

  • Trace every access path: See exactly how access is granted through accounts, groups, roles, policies, permissions, and other authorization relationships.

  • Identify access risk: Find privileged, excessive, dormant, unused, and overly broad access, with the context needed to understand why it matters.

Group membership

See which identities are associated with each group

Finance

Identity provider group

Emily CarterPower BI Service

HR

Identity provider group

Jake Thompson

AI & Service Identities

Identity provider group

claims-copilot-agentrag-servicesvc-customer-portal

Start with an identity or a resource

Investigate access from either direction. See everything an identity can reach, or start with a sensitive resource and see everyone and everything that can access it.

  • Start with an identity: See every connected resource the identity can access, what it can do, and each path that grants that access.

  • Start with a resource: See every human and non-human identity that can access a resource, what permissions they have, and how they got them.

  • See all identities together: Investigate employees, contractors, service accounts, workloads, applications, API clients, and AI agents through the same access model.

Effective access paths

Trace how each identity can reach resources and data

Emily Carter

Human identity

Access group

Finance-ReadOnly

Customer_PII

svc-customer-portal

Application service

Access group

Data-Engineering

Claims_Records
Support_Tickets

claims-copilot-agent

AI agent

Access group

Claims-Assist

Claims_Records

Build one view of access across the enterprise

Access is fragmented across identity providers, applications, databases, data platforms, cloud infrastructure, and custom systems. Ubiq brings those access relationships together so teams can see what each identity can actually access and why.

  • Connect enterprise systems: Bring users, service accounts, groups, roles, permissions, and resources together across enterprise systems.

  • Connect access relationships: Connect groups, roles, policies, grants, and permissions across identity providers, applications, databases, cloud platforms, and other systems.

  • Include custom applications: Extend the graph with custom connectors, APIs, and an open schema for organization-specific authorization models.

From fragmented permissions to effective access

  1. Identity systems

    Users, groups, service accounts, applications

  2. Authorization relationships

    Roles, policies, grants, memberships, permissions

  3. Resources

    Applications, infrastructure, databases, data, repositories

  4. Effective access

    Who can access what, what they can do, and why

Turn effective permissions into least-privilege decisions

Least-privilege analysis compares effective access with the access an identity needs for its job. Ubiq resolves permissions across supported systems so security and IAM teams can trace broad access and give permission owners evidence for a change.

Bring a representative identity, a resource, and the actions that identity should need. Test granting-path accuracy and source coverage before expanding the project. Review authorization-data integration options.

  • Trace excessive access to its source

    Trace direct assignments, nested groups, inherited roles, policies, and grants. Compare the resulting permissions with the person's job or the service's purpose to identify which granting paths need review.

  • Review privileged actions

    Start with a resource to see who can perform sensitive actions and why. Check the source's action definitions, then investigate each identity's other resources and permissions before deciding what should remain.

  • Evaluate dormant and unused access

    Use available account and activity signals to find access that may no longer be needed. Confirm the observation period and signal coverage. Missing activity evidence is not proof that a permission is unused.

  • Include human and non-human identities

    Review users, service accounts, applications, workloads, API clients, and AI agents in the same model. Check access in both directions against the source grants. Analysis extends beyond sensitive data and Ubiq-protected resources.

Answers

Access Intelligence questions

Direct answers about effective permissions, access paths, connected systems, and human and non-human identities.

What is Access Intelligence?

Ubiq Access Intelligence shows who and what can access enterprise resources, what actions they can perform, and why that access exists. It resolves identities, accounts, groups, roles, policies, permissions, and other authorization relationships into a unified view of effective access.

How does Access Intelligence support ISPM?

Ubiq Access Intelligence supports identity security posture management (ISPM) by resolving effective permissions across supported enterprise systems. Teams can investigate what human and non-human identities can access, trace the paths that grant access, and identify privileged, excessive, dormant, unused, or overly broad access when the necessary data is available.

What are effective permissions?

Effective permissions represent what an identity can actually do after direct assignments, group membership, inherited permissions, nested roles, policies, grants, and other access paths are evaluated.

Can I investigate access from both directions?

Yes. Start with an identity to see everything it can access, or start with a resource to see every identity that can reach it. In both cases, Ubiq shows what access exists and the paths that make it possible.

Does Ubiq support non-human identities and AI agents?

Yes. Human users, service accounts, applications, workloads, API clients, and AI agents can be represented in the same access model.

What access risks can Ubiq identify?

Ubiq can identify privileged, excessive, dormant, unused, and overly broad access when the necessary identity, authorization, and activity data is available.

Is Access Intelligence limited to sensitive data?

No. Access Intelligence resolves effective access to supported enterprise resources, not only sensitive data or datasets protected by Ubiq. Sensitive Data Discovery and Runtime Data Protection are optional connected products, not prerequisites for access analysis.

How does Access Intelligence ingest authorization data?

Access Intelligence ingests identity and authorization relationships through supported connectors, custom connectors, APIs, and an open authorization schema. Coverage depends on the systems and authorization data connected to the deployment.

What should an effective-access evaluation verify?

Test representative human and non-human identities and resources in both directions. Compare effective permissions with the actions each identity should need, then verify the direct, inherited, nested, and indirect granting paths against source authorization data. For dormant or unused access, confirm the available account and activity signals and their observation period.

How does Ubiq support least-privilege decisions?

Ubiq resolves effective permissions and traces the paths that grant access. Security and IAM teams compare that evidence with the access each identity needs, then give permission owners the findings to review. Access Intelligence provides the analysis, not automated entitlement revocation, lifecycle provisioning, or privileged-session management.

Does Access Intelligence work independently?

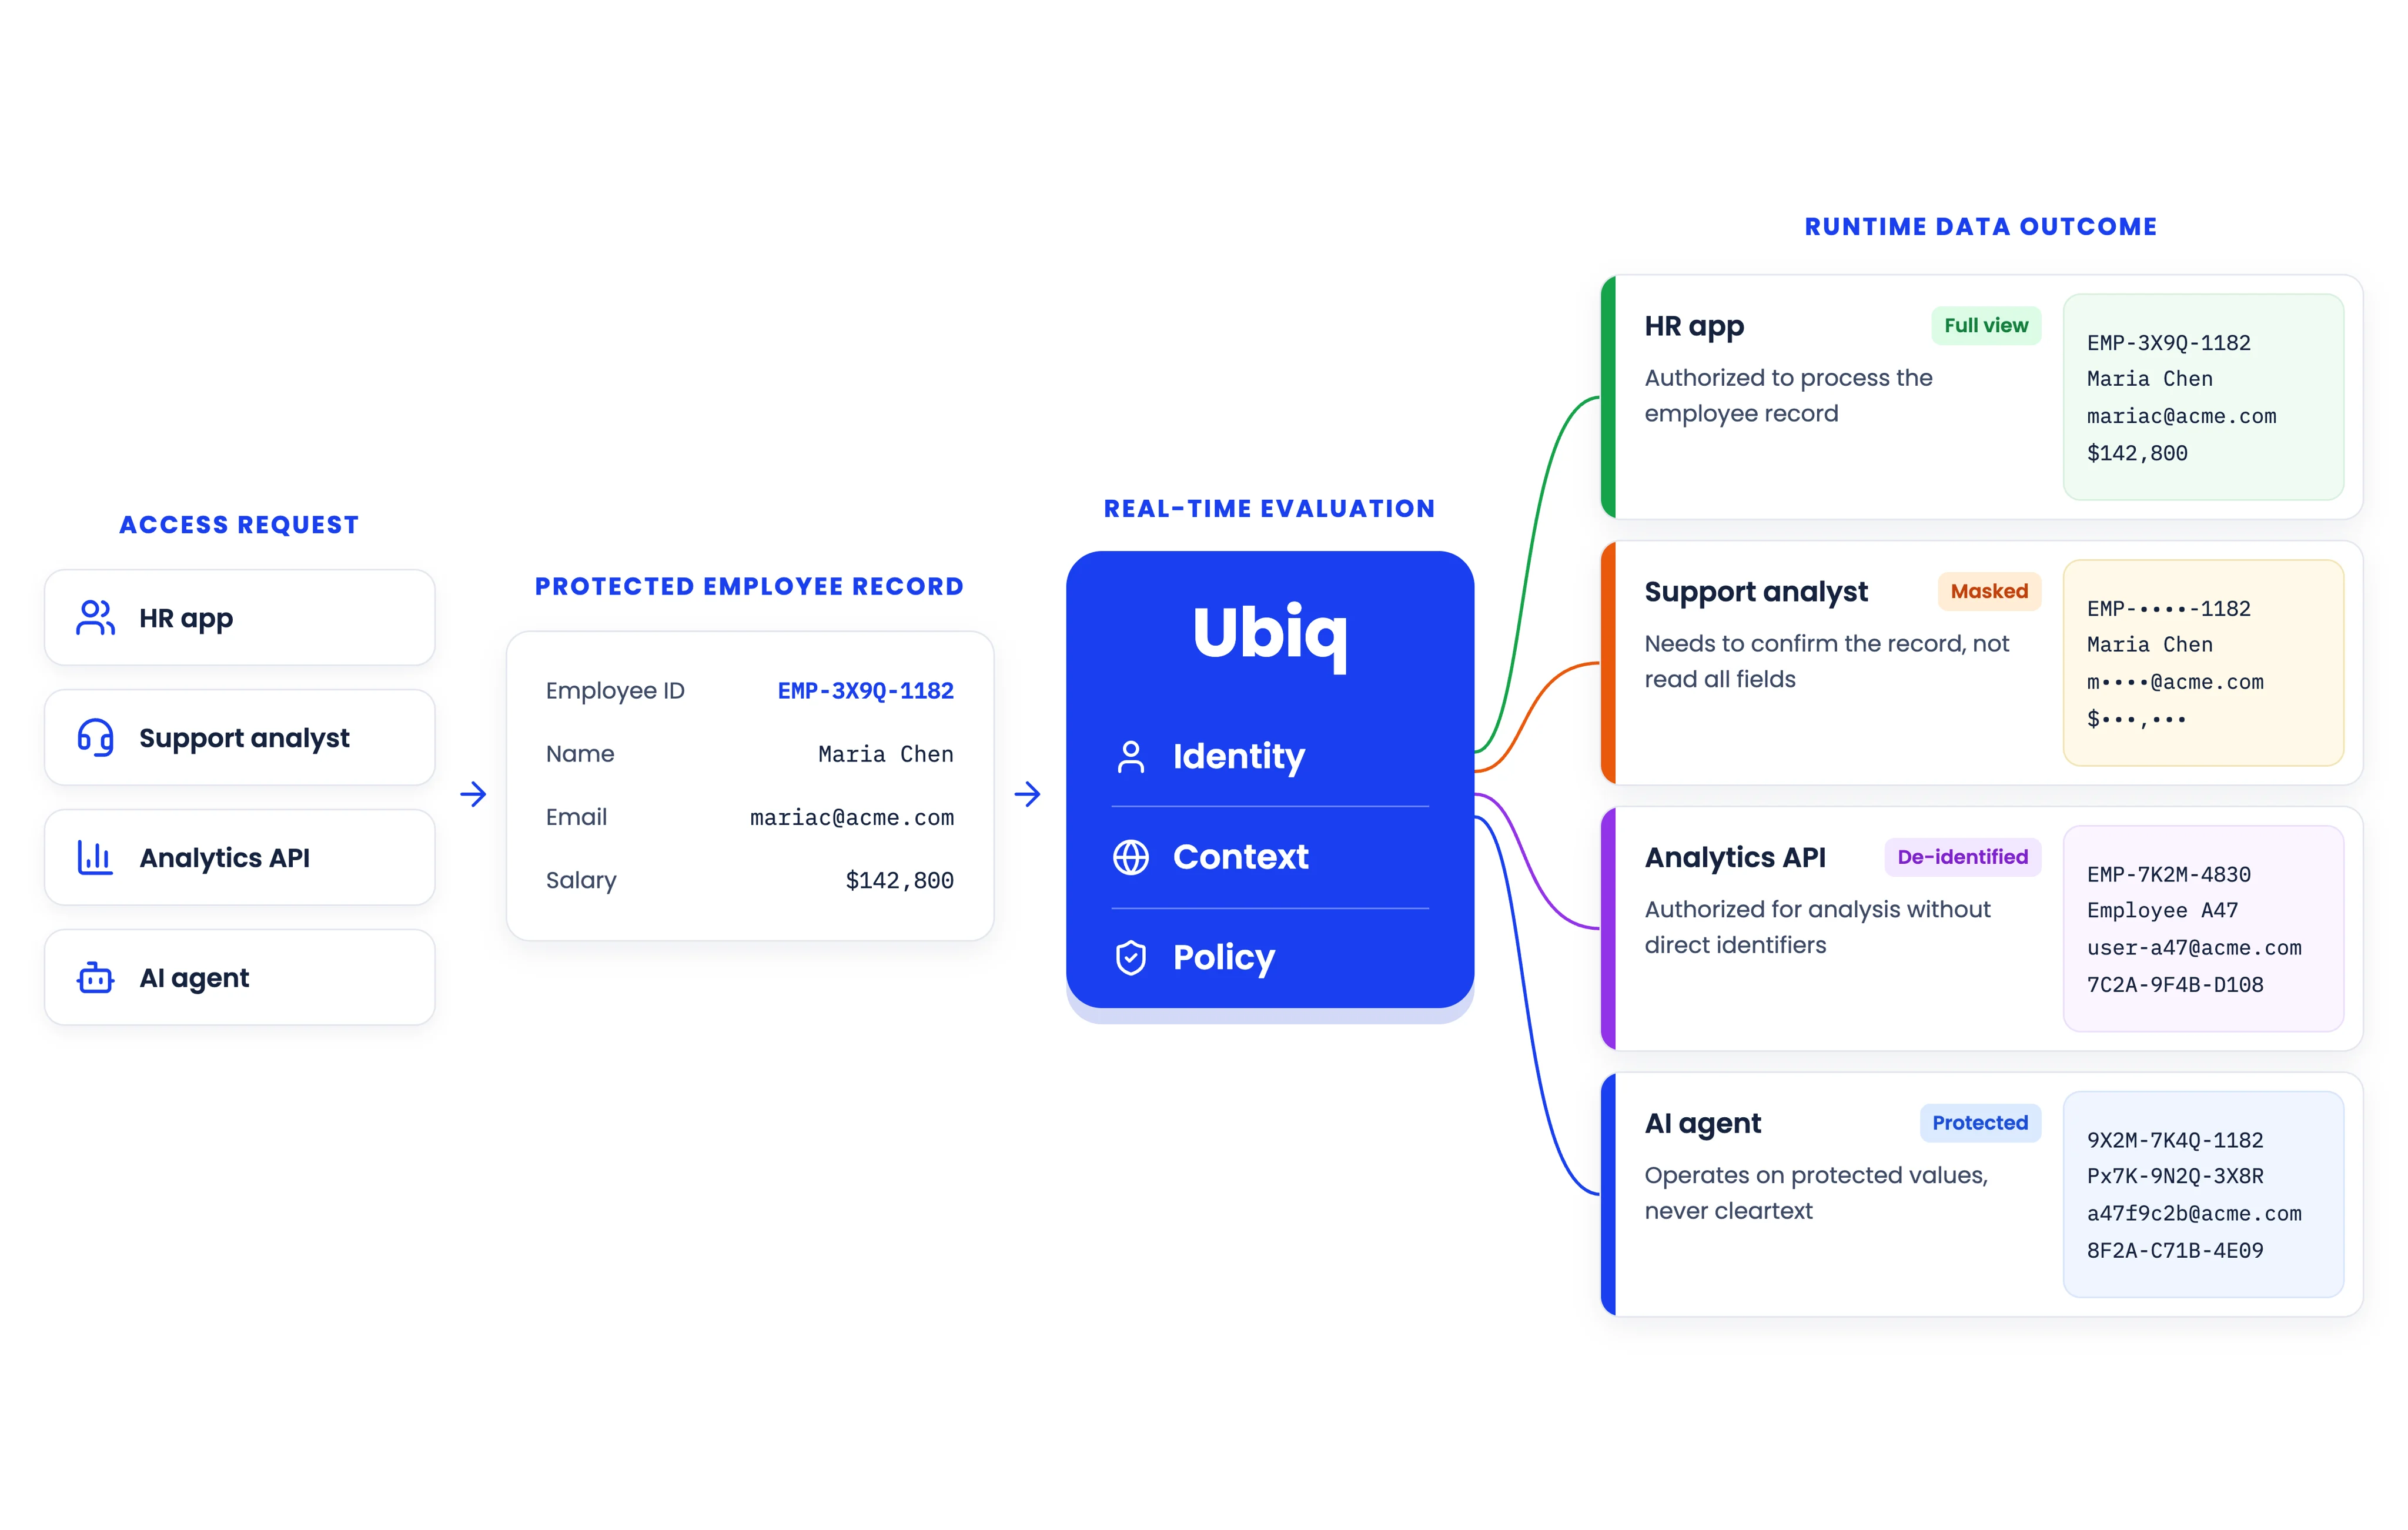
Yes. Access Intelligence can be deployed independently. When used with Sensitive Data Discovery, access can be evaluated alongside data sensitivity. When used with Runtime Data Protection, identity and policy context can also inform what sensitive data an established requester receives.
Additional platform value

Connect access intelligence to data protection

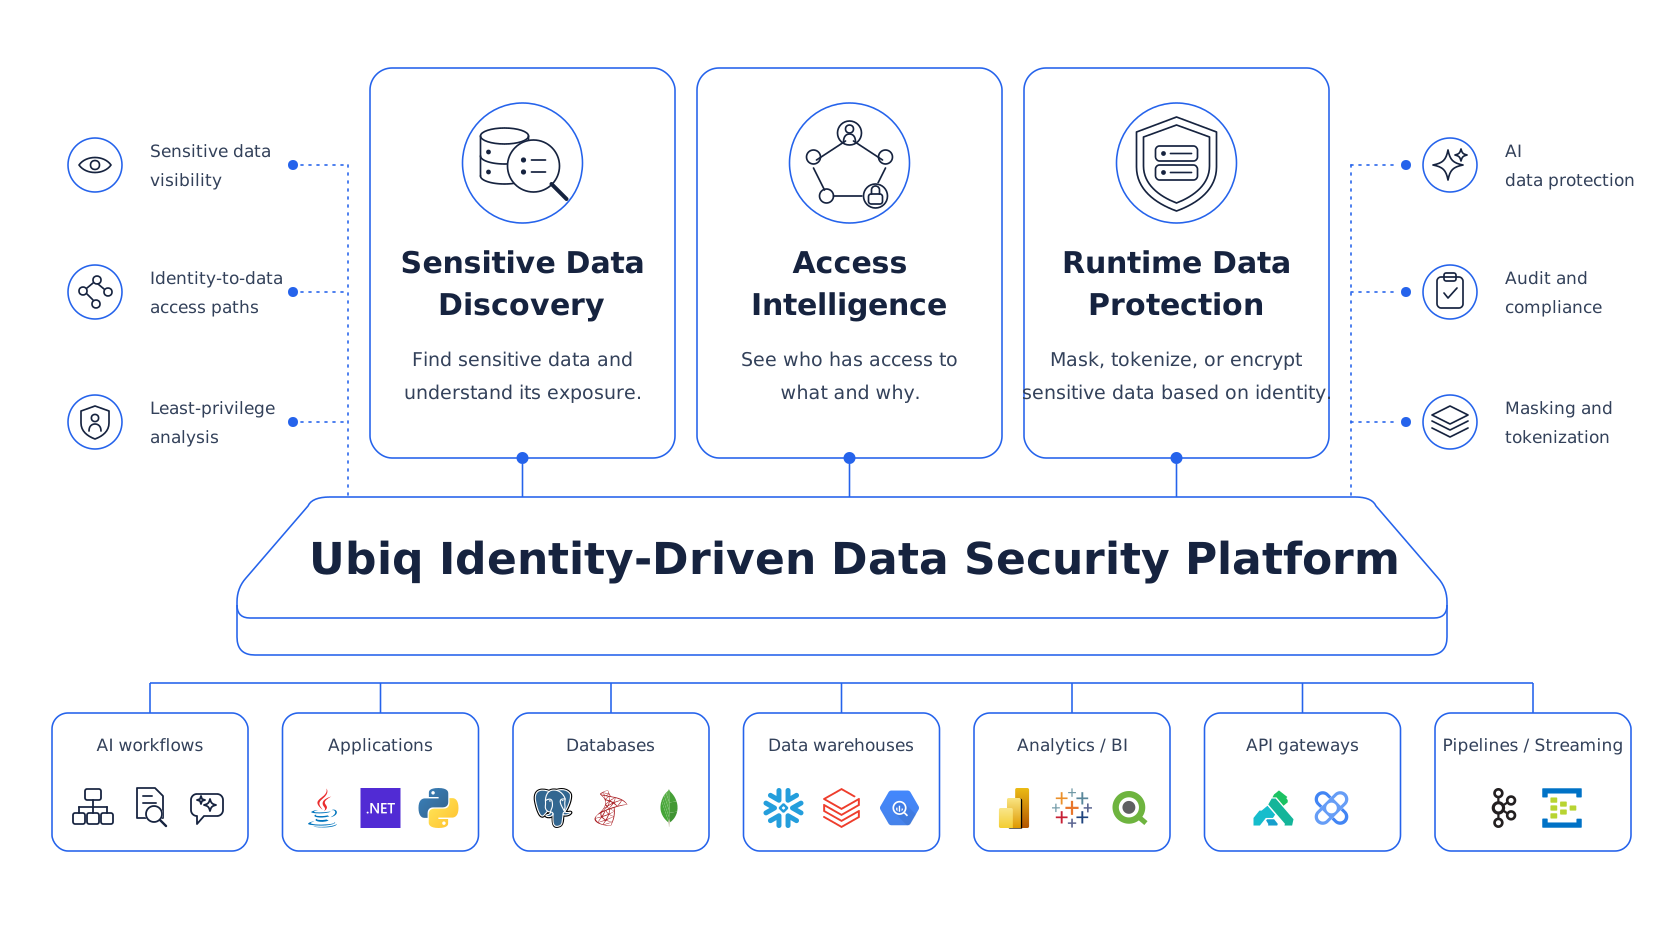
Adopt Access Intelligence independently for enterprise access analysis. Add Sensitive Data Discovery to connect access to sensitive findings, and Runtime Data Protection to control the values each identity receives.

Get a complete picture of enterprise access

Map identities to resources, resolve effective permissions, and uncover access risk across connected systems.

Request a Demo